Offensive security at enterprise scale.
Since 2014
Independent CREST-accredited penetration testing from a cyber security company headquartered in Singapore, with permanent offices in Singapore, Indonesia and Thailand. We help enterprises, banks, and critical sectors expose real risk through adversarial expertise.
Across Southeast Asia
Application security & penetration testing
Used responsibly wherever it improves coverage, speed and consistency
Singapore · Indonesia · Thailand


Two skilled testers, the same system, different findings.
Traditional penetration testing varies from consultant to consultant. Two equally skilled testers reviewing the same system often surface different sets of flaws. That inconsistency is the gap Velocity was built to close.
Velocity gives consultants a structured, test-case-driven path through every engagement, mapped to regulatory standards, with evidence captured at each step. Consultant expertise stays central; delivery becomes consistent, repeatable, and audit-ready.
How Velocity worksDid either consultant find all the flaws?
Offensive security across the modern enterprise.
Penetration Testing
CREST-accredited penetration testing services across Mobile & Web Applications, Infrastructure, Cloud, AI, and IoT Hardware.
Explore service →IoT Hardware Testing
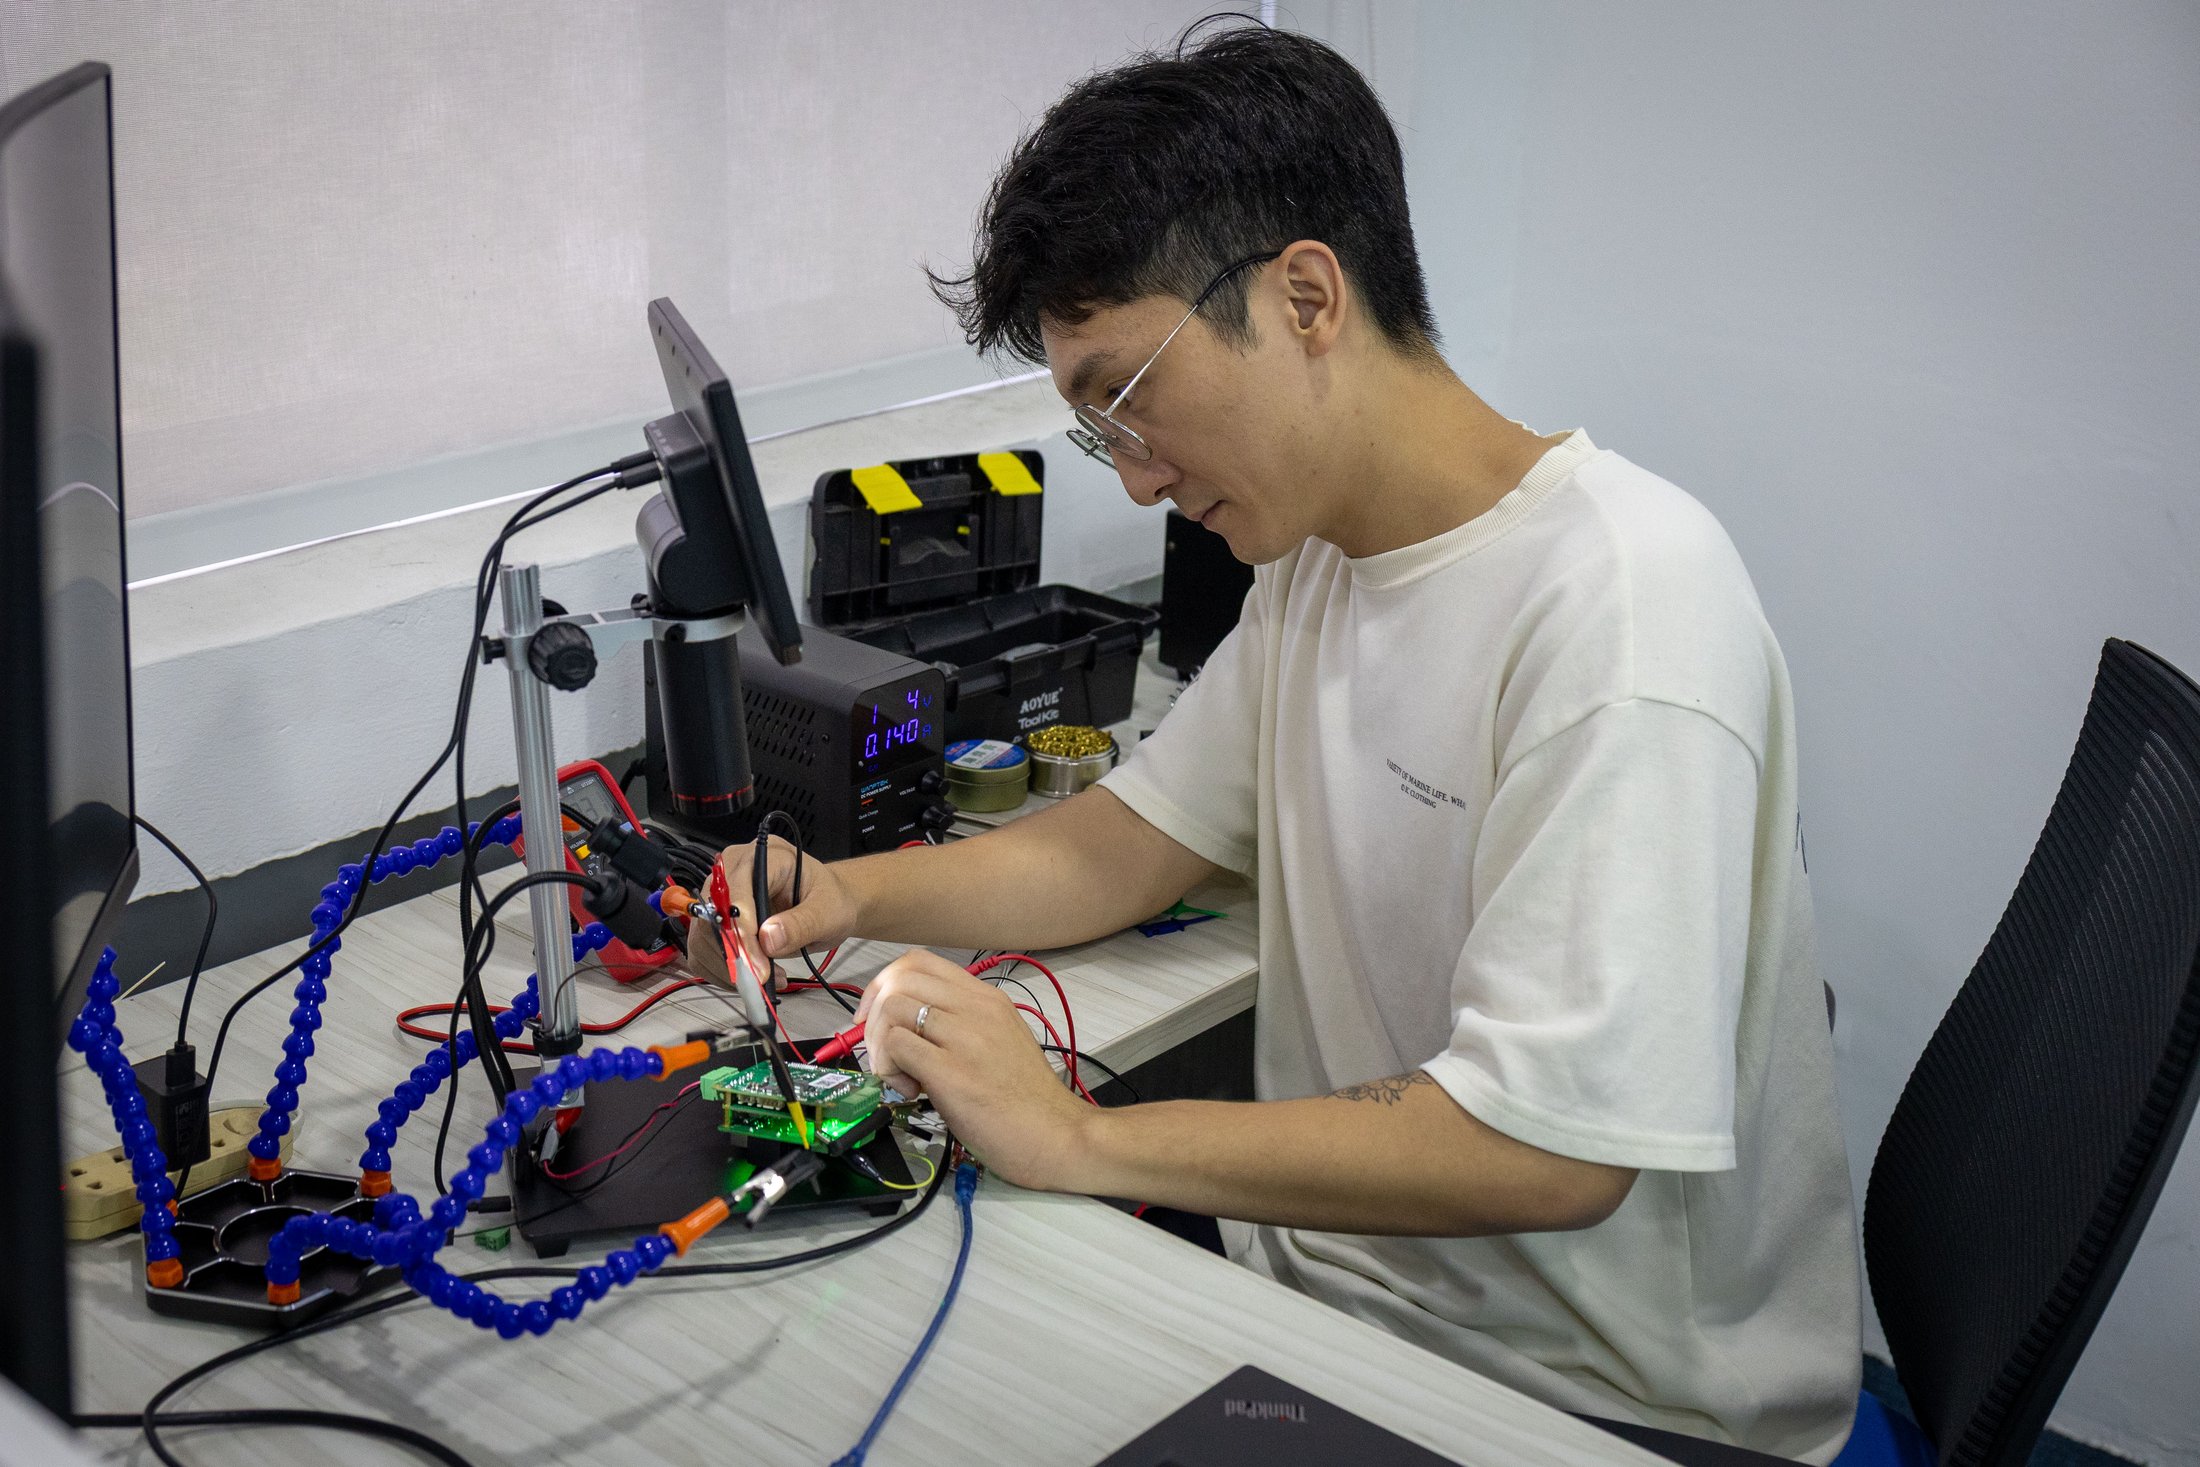
EU Cyber Resilience Act (CRA), Singapore CLS, and SEA-regulator aligned security testing for connected devices, firmware, embedded systems, hardware interfaces, radio protocols, and sensors.
Explore service →Cloud Security
Cloud compliance assessments and platform-specific reviews across AWS, Azure, GCP, and AliCloud.
Explore service →Infrastructure Security
Network vulnerability assessment, security configuration review, and infrastructure-layer hardening.
Explore service →Regulatory Red Team Exercises
Realistic adversary simulation across technology, people, and process, MITRE ATT&CK aligned, scenario-driven.
Explore service →Source Code Security
Static analysis (SAST) and software composition analysis (SCA) for secure SDLC, dependency risk, and license compliance.
Explore service →LLM Testing
Security testing for LLM-powered applications, AI agents, and copilot integrations, mapped to the OWASP LLM Top 10. Prompt injection, agent abuse, data exfiltration, and model integrity.
Explore service →Dark Web Intelligence
Investigate leaked credentials, ransomware exposure, stolen corporate information, compromised systems, and unauthorised access being traded across criminal underground sources.
Explore service →Other Security Reviews
Specialist testing for emerging and high-risk technology, biometrics, blockchain, ATM/CDM, payment terminals, and enterprise COTS platforms.
Explore service →Velocity AI, An augmented testing approach led by CREST-registered consultants.
Larger scopes. More standards. Less time. Velocity AI reads each Velocity test case, executes tools, and captures structured evidence, between sessions, 24/7, with every finding validated by a consultant before reporting.
Consultant in the loop. Every AI-executed test case is reviewed by a CREST-registered consultant before findings are reported.
Industry-standard scanners, fuzzers, and bespoke tools.
AI orchestration engine that reads, executes, and collects.
Velocity, 4,000+ test cases mapped to 100+ standards.
CREST-registered consultants. Scoping. Validation. Reporting.
Vantage Point was a founding signatory member of the CREST AI Charter, on the responsible use of AI in cyber security.
Verifiable, traceable, regulator-ready.
Standards-Based
Every finding traced to a Velocity test case mapped to OWASP, CIS, regional regulators, and sector-specific standards.
Reproducible Evidence
Affected endpoint, prerequisites, numbered steps, payloads, and screenshots, fully reproducible by your engineering team.
Risk-Ranked Findings
CVSS 3.0, 3.1, and 4.0 scoring with full vector strings, plus actionable remediation guidance and configuration examples.
We secure technology-led organisations operating across complex and regulated industries.
Client references available upon request.


Common buyer questions.
What does Vantage Point Security do?
Vantage Point Security is an independent cyber security company specialising in offensive security. We deliver penetration testing, red team operations, source code review, cloud and infrastructure security testing, IoT and hardware testing, LLM testing and dark web intelligence. The group was founded in Singapore in February 2014 and is headquartered there, with operating companies in Singapore, Indonesia and Thailand.
Which countries does Vantage Point Security operate in?
Three. Vantage Point Security Pte. Ltd. in Singapore, PT. Vantage Point Security Indonesia in Jakarta, and Vantage Point Security (Thailand) Company Limited in Bangkok. Each is a separately registered local company with its own security consultants, and each contracts, scopes and delivers work in its own market.
Is Vantage Point Security CREST-accredited?
Yes. The Singapore company holds the group’s CREST accreditation as an approved supplier for penetration testing, and the CREST profile records the Indonesian and Thai offices under it.
What is the difference between VAPT and penetration testing?
A vulnerability assessment enumerates and ranks weaknesses, usually with broad tool coverage. A penetration test goes further: exploiting weaknesses where it is safe to do so, chaining them together, and demonstrating real business impact. VAPT — vulnerability assessment and penetration testing — is the industry term for buying both together, and is how most procurement teams in Singapore and Indonesia scope the work.
How should a company choose a penetration testing provider?
Look for independent accreditation such as CREST, a methodology you are allowed to inspect, consultants who stay on your engagement rather than being substituted, and a report that traces each finding to a specific requirement in a recognised standard. Ask which legal entity holds the contract and which one performs the testing — across Southeast Asia those are frequently not the same company.
Test Your Defences Against Adversarial Expertise
Talk to one of our experts about your next penetration testing needs.